I think people over blow how dangerous it is. Or maybe its better most people dont. I don’t know I know the issues and I take measures to mitigate them. Then if someone gets in they would be limited to vlan. And if somebody gets out of that good wasted so much effort for nothing since I have nothing that would be worth that much trouble.
And before someone says identity pretty sire that has been in so many other leaks overt the years the information is pretty old.


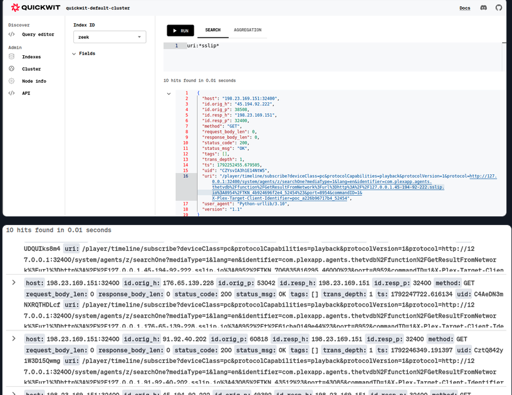
I’m guessing this requires it be exposed to the Internet. Please stop exposing services to the Internet.
That’s pretty much the number one reason people say they won’t move to Jellyfin - the ease of public access.
Even though exposing your shit to Internet is a terrible idea for most people.
I think people over blow how dangerous it is. Or maybe its better most people dont. I don’t know I know the issues and I take measures to mitigate them. Then if someone gets in they would be limited to vlan. And if somebody gets out of that good wasted so much effort for nothing since I have nothing that would be worth that much trouble.
And before someone says identity pretty sire that has been in so many other leaks overt the years the information is pretty old.
Even without data compromise or pivoting, they can still mine crypto on your hardware, launch a ddos, spam email, do botnet stuff, or host CSAM.