The update got released over 2 months ago. So sensible admins should not be getting hit by this.
Also I use Jellyfin btw.
Also I use Jellyfin btw.
Oh god, its the new Arch isn’t it…
No nix is the new arch.
Lol
I’m waiting to see the elusive Arch, Jellyfin Vegan stack in the wild. We know they exist and they are fucking telling everyone
I think it’s not a widely used phrase yet
It definitely is in this community
Everyone talks about Jellyfin, but I just switched to Emby and I couldn’t be happier (no connect cloud stuff). Can someone please let me know why and how I just made the worst decision of my life please.
The main reason is that if you switch from Plex to Emby you’re going from paid licenseware (fully enshittified) to paid licenseware (not fully enshittified yet). It’s like when everyone finally dropped Skype and moved to… Discord. Which hey it’s closed source and owned by venture capital, but it doesn’t suck yet!!! And now in 2026, Discord is what Discord is.
Sure explains why Plex was so cagey and uninformative when they emailed everyone to update their servers a couple months back. Not so much as a CVE report or change set.
A vulnerability? No…. 4 of them. And they stack.
That kind of is the proper way to handle this. You don’t want to hint bad actors where to look and give people some time to update.
As someone who has nearly all internet facing software auto update with watchtower nightly my cortisol is so low
Hackers still doing cryptominers nowadays? C’mon, get with the times, install a LLM model on people’s computers instead.
The cryptomining still potentially pays, the LLMs just cook the user’s hardware.
Running your own crypto miners doesn’t make sense anymore because the cost of electricity. Running a crypto miner using someone else’s electricity on the other hand…
If you want to expose plex to the open Internet (not a VPN) Don’t open the plex port to the internet. Turn off the “remote access” setting and run it behind a reverse proxy instead.
Am not sensible admin. Though I did just run a backup and update. How likely am I FUBAR?
Edit: I run Plex on a dedicated proxmox VM. Theoretically I could nuke it and start over with my Plex database file. Though there’s some config I’d have to do again and I don’t want to
I was also impacted, you need to remove the payload that got dumped:
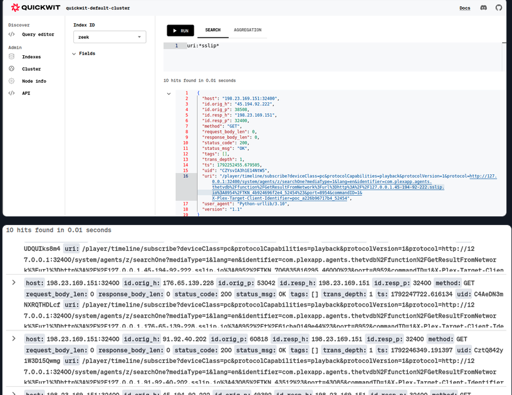
Payload: /tmp/.pxb/{curl,wget}, /tmp/.spid
Two processes named khungtaskd / cron
They also stole your admin token so go to the Plex UI and log out of all devices for whichever account has ownership of the instance.
Then you can reclaim ownership and it resets the admin token.
You should likely be fine, I didn’t have any crypto miners on mine, it was just in a docker instance and didn’t have access outside of it. I would be much more worried if it was a direct install on a main PC.
Also install watch tower
Second post I’ve seen mentioning watchtower… it quit being developed about a year ago and is read-only now. I quit recommending it since it’s not being actively developed any longer.
It was forked months ago and is actively developed https://github.com/nicholas-fedor/watchtower/
I’m guessing this requires it be exposed to the Internet. Please stop exposing services to the Internet.
That’s pretty much the number one reason people say they won’t move to Jellyfin - the ease of public access.
Even though exposing your shit to Internet is a terrible idea for most people.
I think people over blow how dangerous it is. Or maybe its better most people dont. I don’t know I know the issues and I take measures to mitigate them. Then if someone gets in they would be limited to vlan. And if somebody gets out of that good wasted so much effort for nothing since I have nothing that would be worth that much trouble.
And before someone says identity pretty sire that has been in so many other leaks overt the years the information is pretty old.
Even without data compromise or pivoting, they can still mine crypto on your hardware, launch a ddos, spam email, do botnet stuff, or host CSAM.