
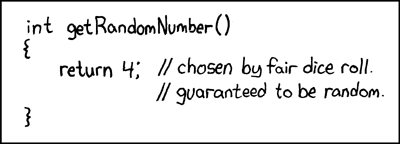
Astonishingly, the private keys were 4, 56, 66, 115, 155, 156, 230, 237.
exploiting compromised certificates requires an active adversary-in-the-middle attack, meaning the attacker must act as a proxy between two TLS parties and receive encrypted traffic, decrypt it, reencrypt it, and send it to the other party. Such capabilities, in some cases, are usually limited to only the most well-resourced attackers. People with control of a local network—at a coffee shop, university, or other organization—face much less of a challenge.
https://emudhra.we-have-a-problem.com/
I think that this isn’t really getting the right attention, about what a massive WTF situation this is…
its a 384 bit certificate and this is the private key
00:00:00:00:00:00:00:00:00:00:00:00:00:00:00:
00:00:00:00:00:00:00:00:00:00:00:00:00:00:00:
00:00:00:00:00:00:00:00:00:00:00:00:00:00:00:
00:00:04that is just fucking NUTS
Phew to think how close it is to my private key
4E:65:76:65:72:20:67:6F:6E:6E:61:20:67:69:76:
65:20:79:6F:75:20:75:70:20:4E:65:76:65:72:20:
67:6F:6E:6E:61:20:6C:65:74:20:79:6F:75:20:64:
6F:77:6E
is much more secure.
LOL, People are never gonna give this up.
I’m too lazy to do the math. Does that translate to the URL?
No, it is a string of text. “Never gonna give you up never gonna let you down”
that’s a very long way to spell the random number 4
It’s like winning the lottery
Winning the lottery is (ballpark) 1 in 10^9, so generating a key below a million is like winning 11 lotteries in a row, while buying 1 ticket in each.
They wouldn’t know how you’d done it, but I think you’d be arrested, with valid probable cause.
Okay, that’s fun and scary at the same time.
The article links to a webpage,
https://emudhra.we-have-a-problem.com/
That shows if your browser is still using those certs, and though it says Firefox has already updated, maybe it hasn’t reached mobile yet as it shows I’m using them all still.
I guess I won’t connect to anything important for a few days.
My Firefox mobile got green ✅
Maybe try manually updating through the app store
As noted, most browsers have already blocked the intermediate certificates. The exception appears to be Edge running on Windows 10, which at the time this article went live was still connecting to 12 vulnerable hosts.
LOL
So if my understanding is correct, to be exploited the attacker would already need to be in a position to intercept your traffic, but this means when they do they can effectively impersonate anyone.
This could actually be an interesting attack vector for hacking IOT devices. If you control the DNS server the device connects to you can get it to trust literally anything.
Wasn’t the Gamer’s Nexus video on LG spy TVs, saying that the telemetry traffic is protected by SSL and thus they couldn’t figure out exactly what was sent? Would they be able to use the leaked keys to decrypt the traffic?
That should be possible yes, depending on how those TVs handle their cert stores.
wait how would that work? don’t LG TVs use a random CA that likely isn’t eMurdha?
Yup.
These days, a lot of firmware blobs are also signed with the vendor’s key, so you’d still need to get past that hurdle.
Adversary-in-the-middle = man-in-the-middle?
Yes, it’s the same as mitm. I get that it’s to avoid gendering the term but it doesn’t really roll off the tongue or preserve the existing abbreviation. I’ve heard the alternatives: machine in the middle, mallory in the middle or, my favourite, Malcolm in the middle.
Man is a gender neutral term
Only in some obsolete or deprecated contexts.
Everyone says mankind.