- cross-posted to:
- technology@lemmy.ml
- cross-posted to:
- technology@lemmy.ml
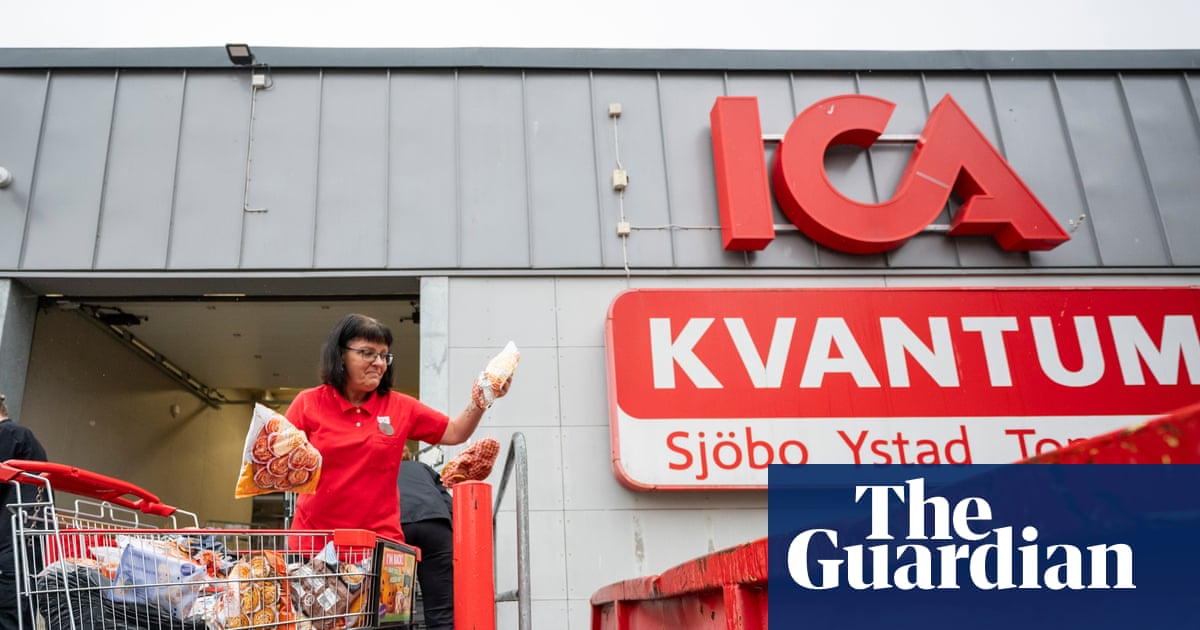
Chains in Sweden, Belgium and Luxembourg say fridge temperatures rose overnight, similar to hack of French stores
Supermarket chains in Sweden, Belgium and Luxembourg have said the temperatures of their refrigerators and freezers in dozens of stores rose overnight, prompting fears of a cyber-attack similar to one that caused millions of euros of food losses in France.
Sweden’s Coop chain told the daily Aftonbladet on Monday that six of its stores had been affected, while ICA said it was “aware that a limited number of stores were affected by an incident overnight which impacted their refrigeration and freezer systems”.
The vulnerable firmware uses the current date as an admin password, and the vulnerability is long known. But the more important question is why these systems are still not connected through an VPN, which is an requirement in any serious corporate environment. This second wave can only happen in businesses that don’t actually have an IT department worth the name, because the first round was already a pretty big news story which should have prompted hectic activity in those departments.
So they left the password default, wow.
From my own personal experience a lot of IT departments don’t know what is on their networks when it comes to building controls and a lot of times it’s just an open port so that maintenance can remote in because there’s no exposed company data. Until someone figures it out and costs the company lots of money.
It’s such a common problem that my employer actually created a whole new division to offer a service just for plugging holes in networks cause specifically by building controls.