I still find it funny that in the distant past an engineer thought pasted commands should have some ~~ characters added, so the user has to delete them & think about their actions while pressing their arrow or various faster ctrl+ keys …
Oni-chan~~
You should really place a /j somewhere before someone thinks they’re screwed
The community it’s posted in is a bit of a giveaway, isn’t it?
How dare you overestimate my intelligence.
I thought I was screwed
Holy shit, my computer is infected. I opened my terminal and typed “sudo ls -halR /” and it showed me every file on my computer. Oh my god.
I just tested this exploit, I was easily able to remove the french language pack by typing “rm -fr /*”
Don’t forget the —no-preserve-root flag or you’ll get an index out of bounds when deleting the recipe for five-root-puree
This flag is fortunately not needed as /* ensures root recipes are preserved. It’s just that anything below isn’t.
Okay. I briefly ate the onion, on this one. It tastes like sysadmin tears.
I had a msg to my team drafted before I realized I was a fucking idiot.
Save it for April 1.
in my defense, my team is always trying to be mr. achiever and drop the latest vulnerability. I got a glimpse of this one and got excited since I hadn’t heard of this “new named threat”. when I tried reading further to prepare my draft… the reach and exposure of this vulnerability became clear.
also, to mitigate this, we’d have to hotpatch layer 8.
How is it in your defense when you were going to do it to them?
justifying my behavior because I was motivated by the aforementioned external behaviors by establishing their trends of beating me to the aforementioned punch.
WOOO I need to let autocorrect hit that aforementioned word again yeah soo satisfying.
Duct tape works a treat for that!
I’ve sent a company wide email telling everyone I don’t want to be sysasmin anymore.
It has nothing to do with the CVE
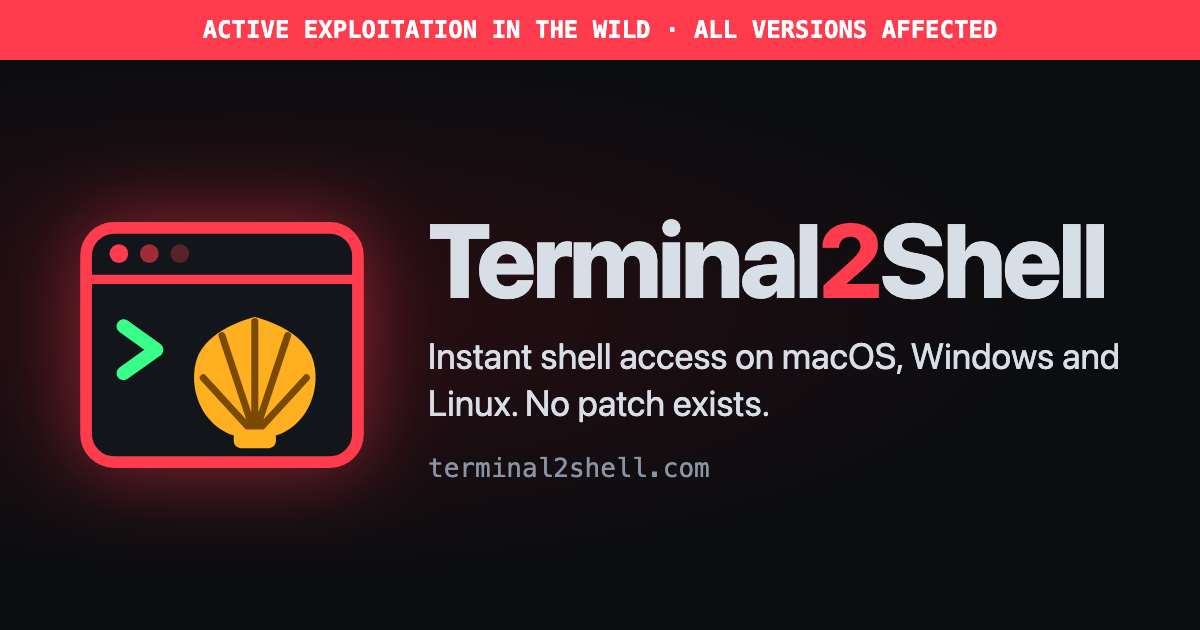
I was fooled until I saw the CVSS score of 11 on a scale of 0 to 10.
I only figured it out because I read your comment.
That’s why I confessed. I’m glad to help.
I’m here cautiously making sure it’s a joke that I don’t understand. Problem exists between keyboard and seat.
Not even that, it’s not a problem at all. They’re just saying that when you open a terminal program you get access to the shell. That is exactly the point of a terminal program. It’s a bit like “exclusive, shocking report: water is wet!”
I mean, I guess part of the joke is if an attacker can get into your computer they can do nefarious things, but that’s not as funny.
Microsoft Paint: Not affected. Thank God.
Unless you have allowed the AI features to install
I’m tired boss
I work at google just shut off every server to protect us. 👍
I took the “us” in your statement to be “humanity” and it sparked an unexpected feeling of hope.
Just tried it out. It is real. And really simple to do.
Scary stuff. Tossing my machines in the bin tomorrow.
I’m not taking any chances. I’ve already tossed
bashinto the/bin/Uh oh I tossed mine in sbin. What do?
Getting a shell is bad, but what makes this worse is the insecurity of popular Linux tools that can be used for privilege escalation.
The
sudoprogram has had a known vulnerability since its inception. The developers are incompetent. In some configurations, all you need is the user’s password and you can execute arbitrary code as root. Sometimes, no password is needed at all.That’s why there’s no
sudoon my system, onlydoas.sudo is so broken, automatic privilege cloning of any user
slop :)
Nobody show this to my boss please, they’ll be asking me why I haven’t fixed it yet
If he says he’s there to upgrade the computers, don’t let him in.
Phew! Just got done patching all my servers. The main IOCs are
- C:\Windows\System32\cmd.exe
- /bin/bash
- /bin/sh
So zsh is good? /s
According to the report, zsh is even worse
2009 zsh adoption grows. Now the shell is also pretty, which researchers believe lures more victims.
nushell, ash, elvish, dash, powershell, …
powershell is good because no hacker can be bothered typing that much to get anything to work ;)
They have aliases for multiple commands (such as
cd,ls,curl, likelycat), so I’d still be careful 😬Security by utter absence of usability
I’m taking some admin/security courses and powershell was touted as “it’s so easy to make your own scripts to save time!”. I was just like, “the fuck Koolaid are you drinking?”
pwsh
Was the command separated by dashes or case change? Let me che…ange to something else.
Given simple primitives and runtime permissions, a skilled hacker can even bootstrap one of these “shells” from scratch, underlining the continued importance of banning math and computer science education in our schools.